Access for the task.
Gone when it’s done.
Replace standing admin with access that is requested, approved by the person who owns it, and revoked on its own. Grants reach into the app itself, not only an identity provider group.
The problems this solves.
Former employees still have access
The engineer leaves. Her agents keep running on her credentials. Her local admin in Snowflake and the service account she created in 2023 still work.
Audits take weeks and get rubber-stamped
Agent and app access gets certified, if at all, by a generic admin with no idea what the identity does. Every cycle starts from scratch.
Every one of these has the same root cause: nobody owns it. See all six problems
The real screens.
Captured from a test tenant. Your tenant looks the same with your data in it.
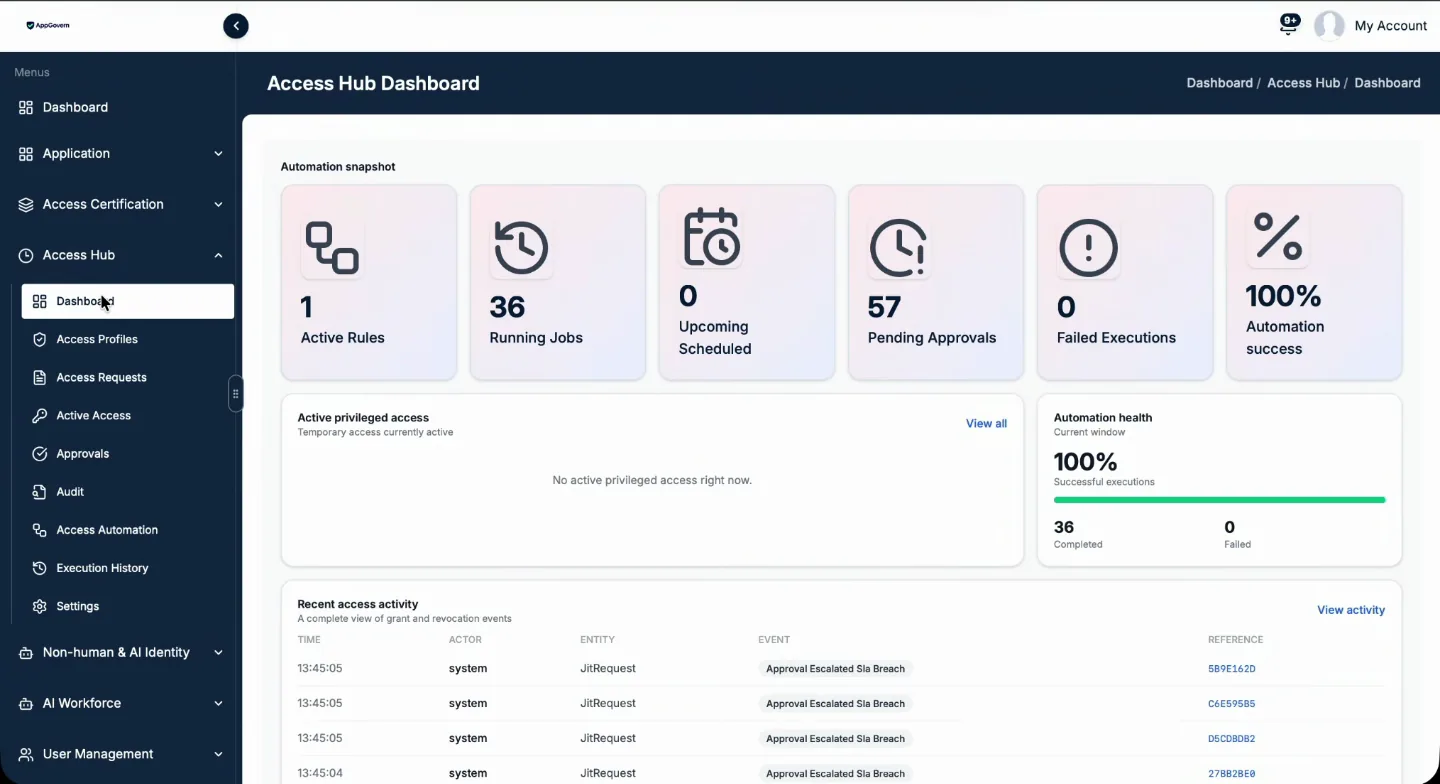
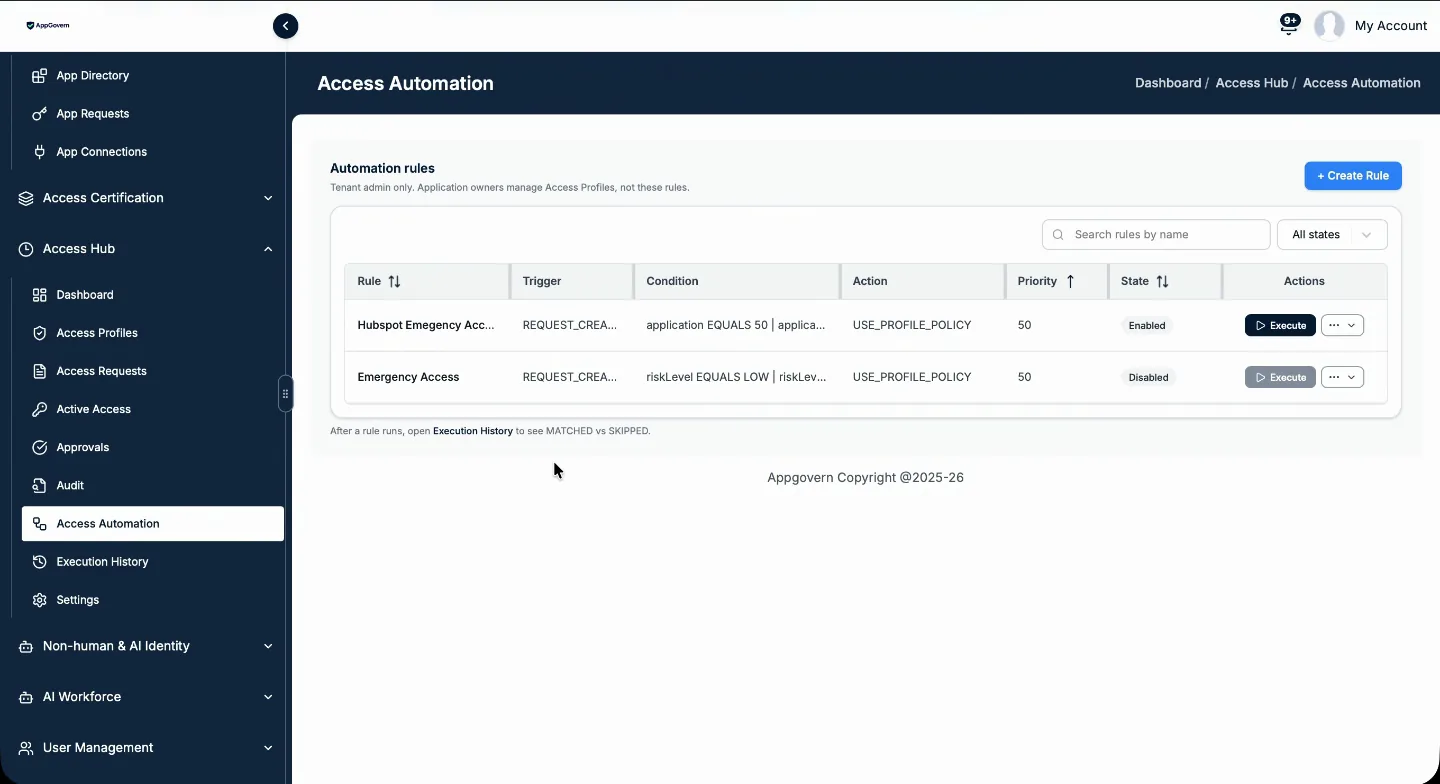
Request, approve, expire.
Define the access levels once.
Each app gets access profiles: read-only, super admin, billing admin, or whatever the app offers. Requests pick from the list. Eligibility rules decide who can see each option.
- Grant into an identity provider group, a role or group inside the app, or an AppGovern role
- Automatic, manual, or ticket-based grant
- Create the account if it does not exist
Approved by the person who owns it.
Approval goes to the owner of the access profile, which by default is the app owner. Justification can be required. Escalation and multilevel approval are settings.
- Single or multilevel approval
- Break glass profiles with their own rules
- Every grant, approval, and expiry in one log
The weekend patch window, without the ticket.
Access automation rules grant on a schedule, a trigger, or an API call, with conditions and templates. The patching team gets database admin every second Saturday, noon to four, and loses it at four.
- Scheduled, manual, request-created, or API triggers
- Templates for common windows
- Active access and execution history
Request what your team already has.
Peer Intelligence shows what access people in similar roles hold, so an employee or manager can work out the access they need and request it. The owner still approves.
- New hires start from what their team holds
- Fewer back-and-forth tickets
- Every request still goes to the owner
Fewer standing privileges, fewer things to review. When standing admin access becomes Just-in-Time, the next certification has far fewer admin entitlements in it. Certification still covers break glass accounts and everyday access.
Questions about Just-in-Time access
Does Just-in-Time go through the identity provider or the app?
Can agents and service accounts get Just-in-Time access?
See it in your own tenant.
Free 14-day proof of concept. Read-only, success criteria agreed before we start, readout on day 14.