Every app. Every identity.
One ownership model.
AppGovern governs the applications you run, the people and local accounts inside them, the AI agents that act in them, and the service accounts behind all of it. One data model, one owner on each.
The problems this solves.
Sensitive data gets leaked
Employees connect agents and tools to company data from personal accounts, IDEs, and browser extensions. Security finds out from a bill or a breach.
Incident response starts from scratch
An agent misbehaves, a service account is compromised, an app is breached. The first hour is spent finding out who built it, who owns it, and who can turn it off.
See the problemEmployees are scared to participate
Teams hide the agents and tools they built because the last one got shut down. The identities you most need to see are the ones nobody registered.
See the problemFormer employees still have access
The engineer leaves. Her agents keep running on her credentials. Her local admin in Snowflake and the service account she created in 2023 still work.
Nobody owns the decision to retire it
Bot accounts, agents, and apps unused for 90 days still hold access, and the renewal still auto-pays, because nobody owns the decision.
Audits take weeks and get rubber-stamped
Agent and app access gets certified, if at all, by a generic admin with no idea what the identity does. Every cycle starts from scratch.
Every one of these has the same root cause: nobody owns it. See all six problems
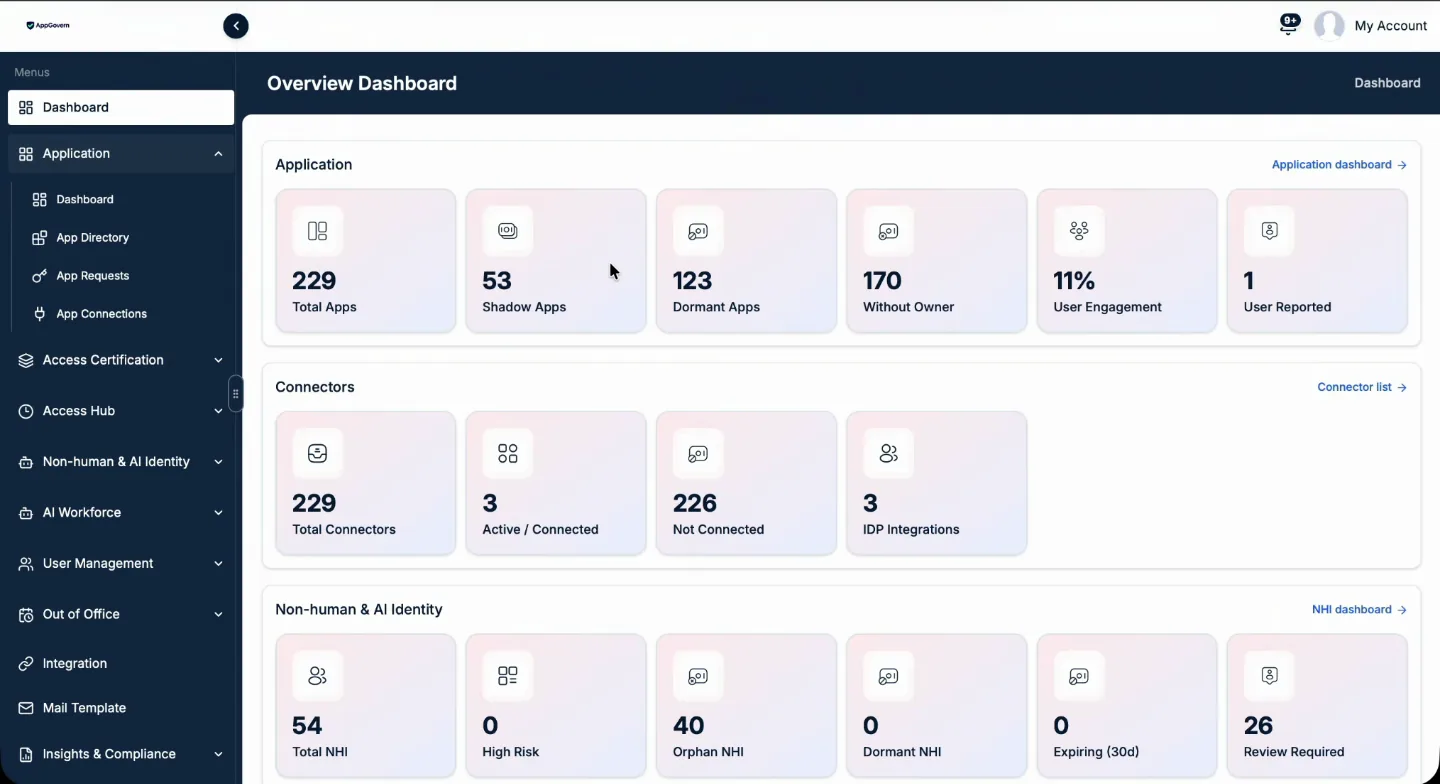
The real screens.
Captured from a test tenant. Your tenant looks the same with your data in it.
Four mechanics, applied the same way to everything.
The method is the same for an app, a person, an agent, and a service account. That is what makes one platform possible.
Find them
Apps from your identity provider and shadow signals. Local accounts from inside the apps. Agents and MCP servers from their configuration and footprint. Service accounts against HR and pattern rules.
Name an owner
A person accepts accountability in writing, timestamped. When there is no owner, the platform proposes one. When the owner leaves, the search runs again.
See what they reach
Every app each identity can touch, and for agents, through which MCP server and with which tools. Risk scored against your rules.
Make the owner sign off
Certification by the owner, the manager, and the employee. Access for a task expires on its own. Every decision is logged.
Govern every identity, human or not.
Built on what you already run.
See it in your own tenant.
Free 14-day proof of concept. Read-only, success criteria agreed before we start, readout on day 14.