Just-in-Time access now reaches inside the app, approved by its owner. See how it works
Platform
Solutions
Why AppGovern
Pricing
Resources
Watch demo
Resources / 7-minute demo

The whole platform in seven minutes.

Apps found, local accounts surfaced, agents mapped, owners accepting, a Just-in-Time grant expiring, and a certification completed.

In the product

The screens from the demo.

Captured from a test tenant.
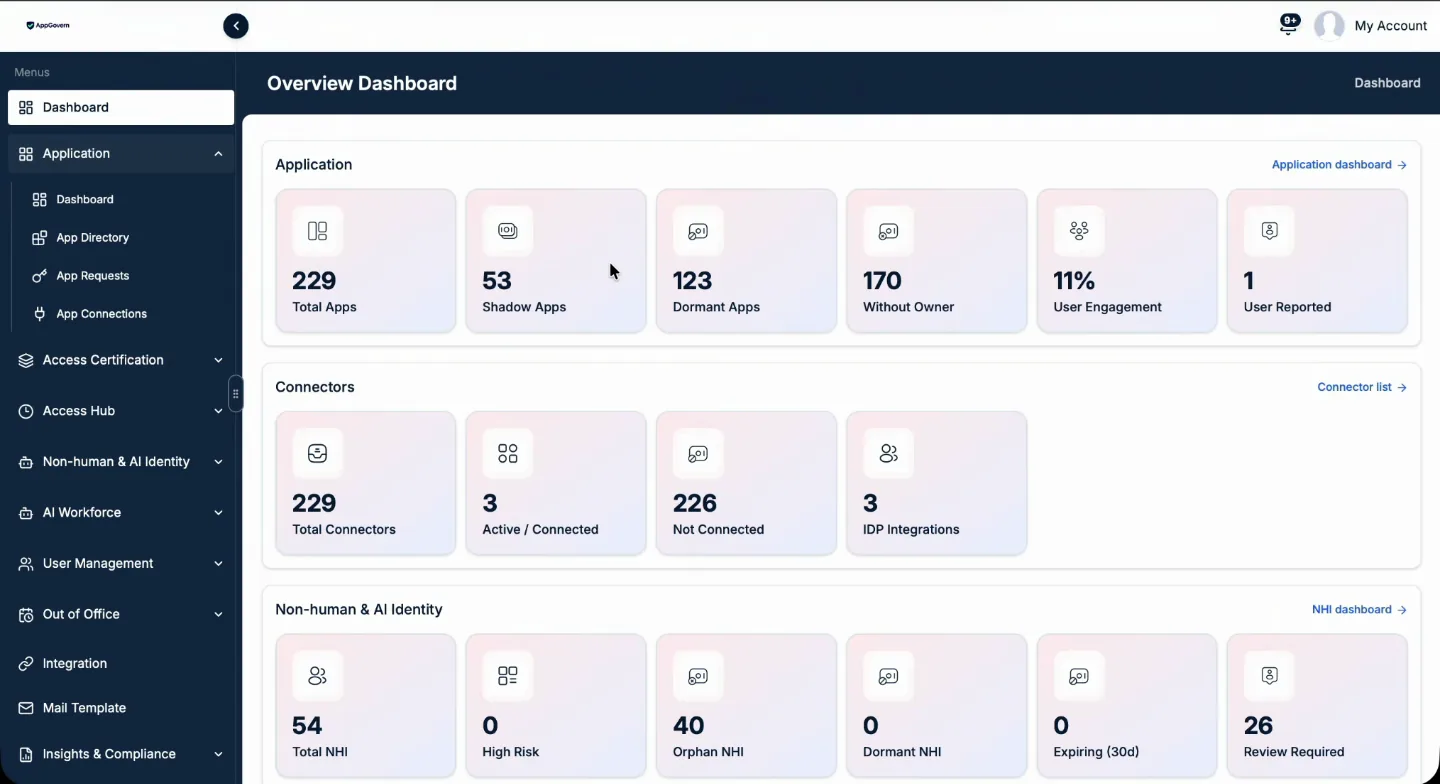
Overview dashboard: applications, connectors, and non-human identities on one screen.
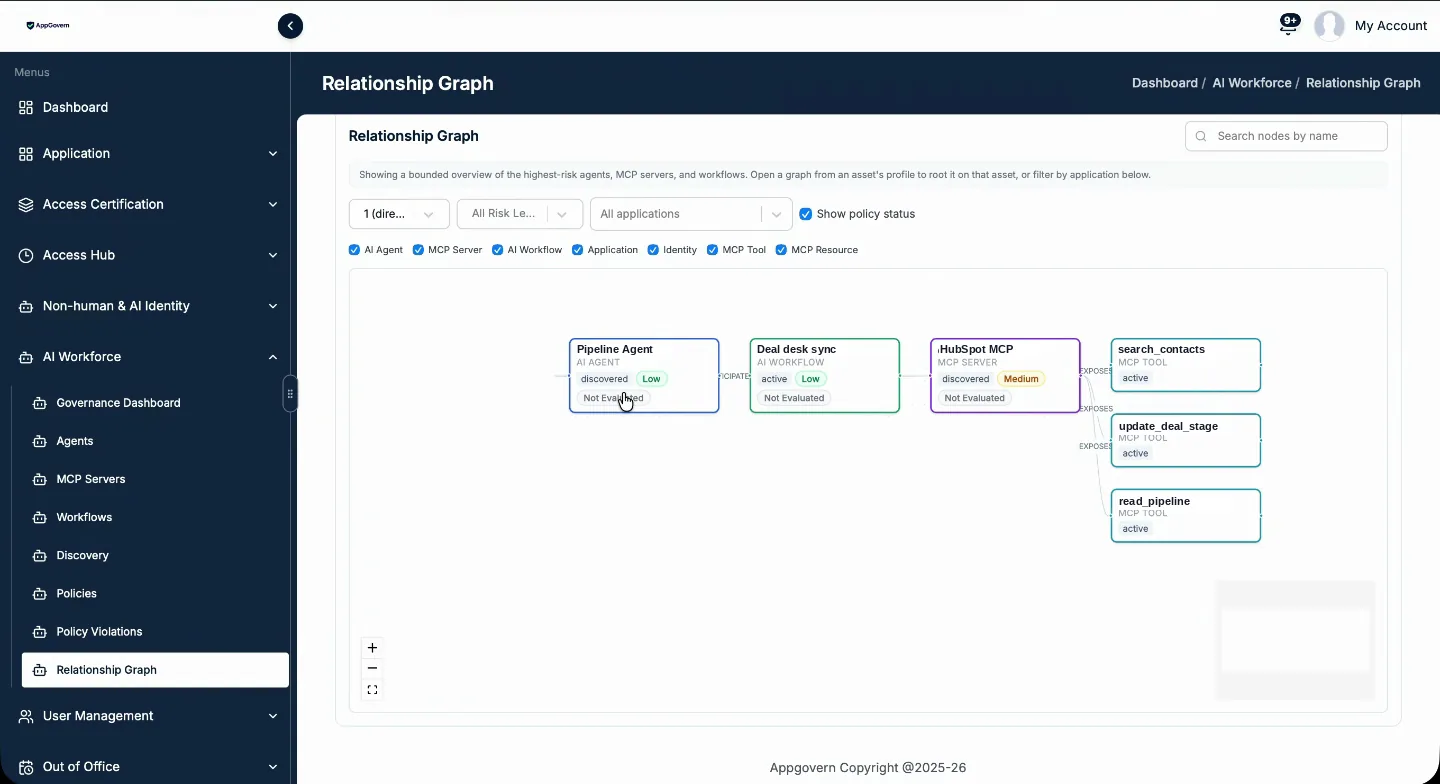
Relationship graph: agent, workflow, MCP server, and tools.
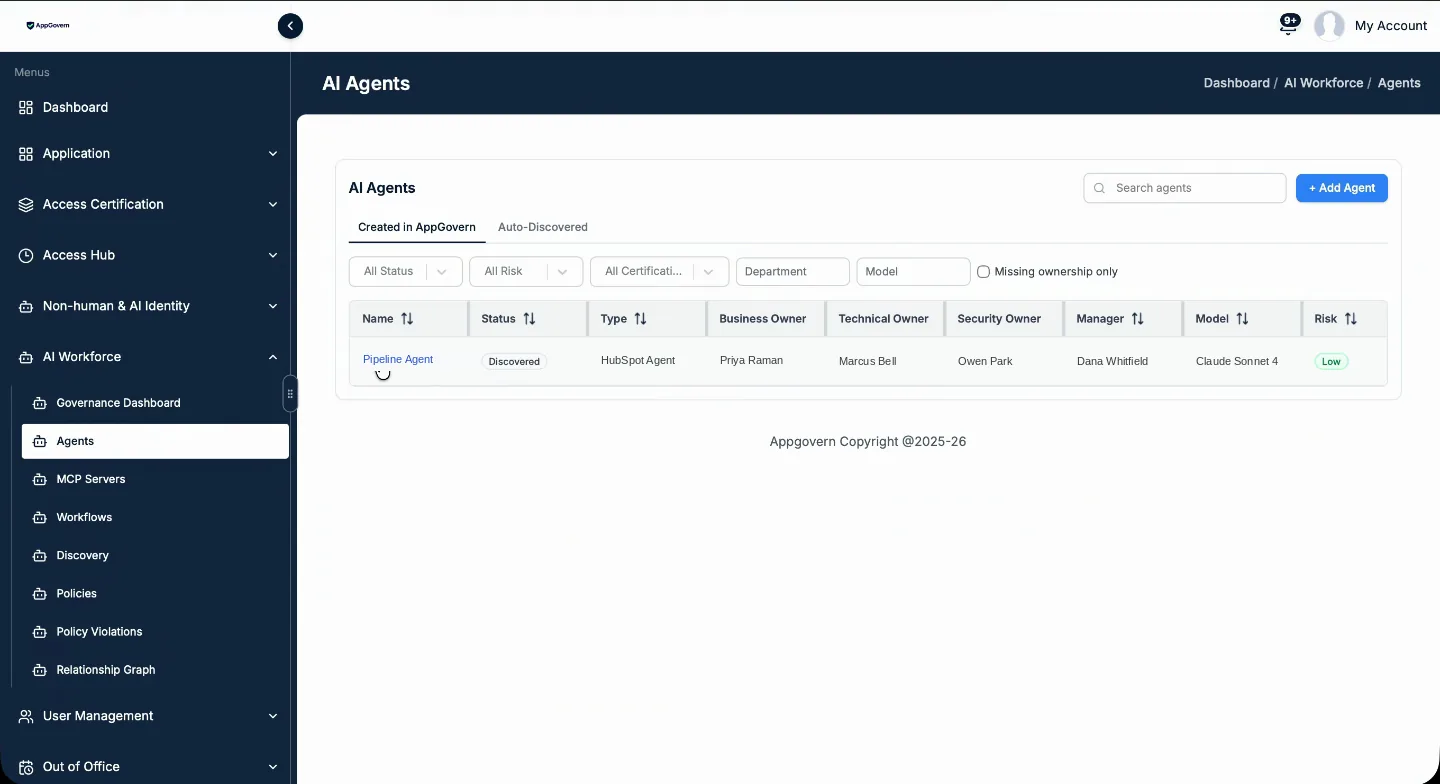
AI agents with type and business, technical, and security owners.
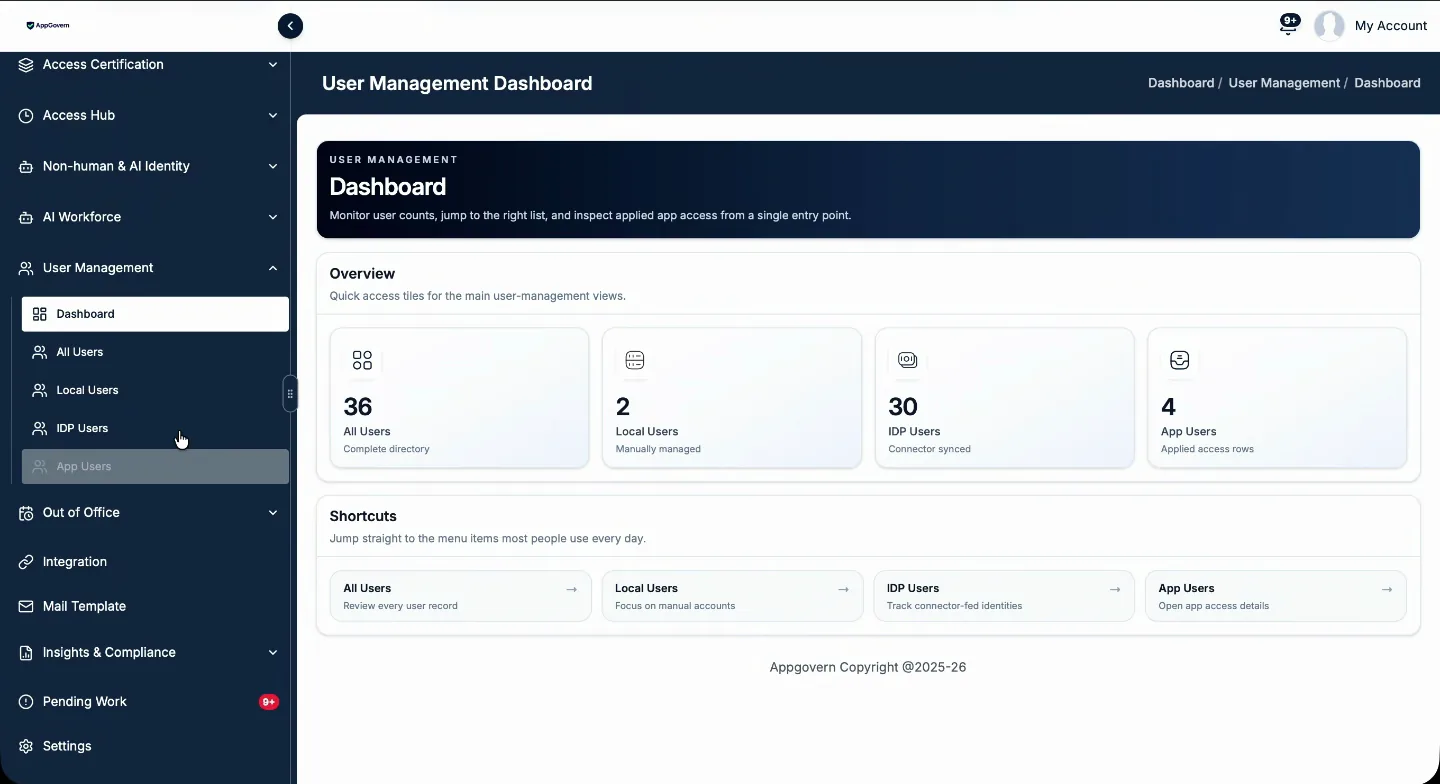
User management: identity provider users, local users, and app users.
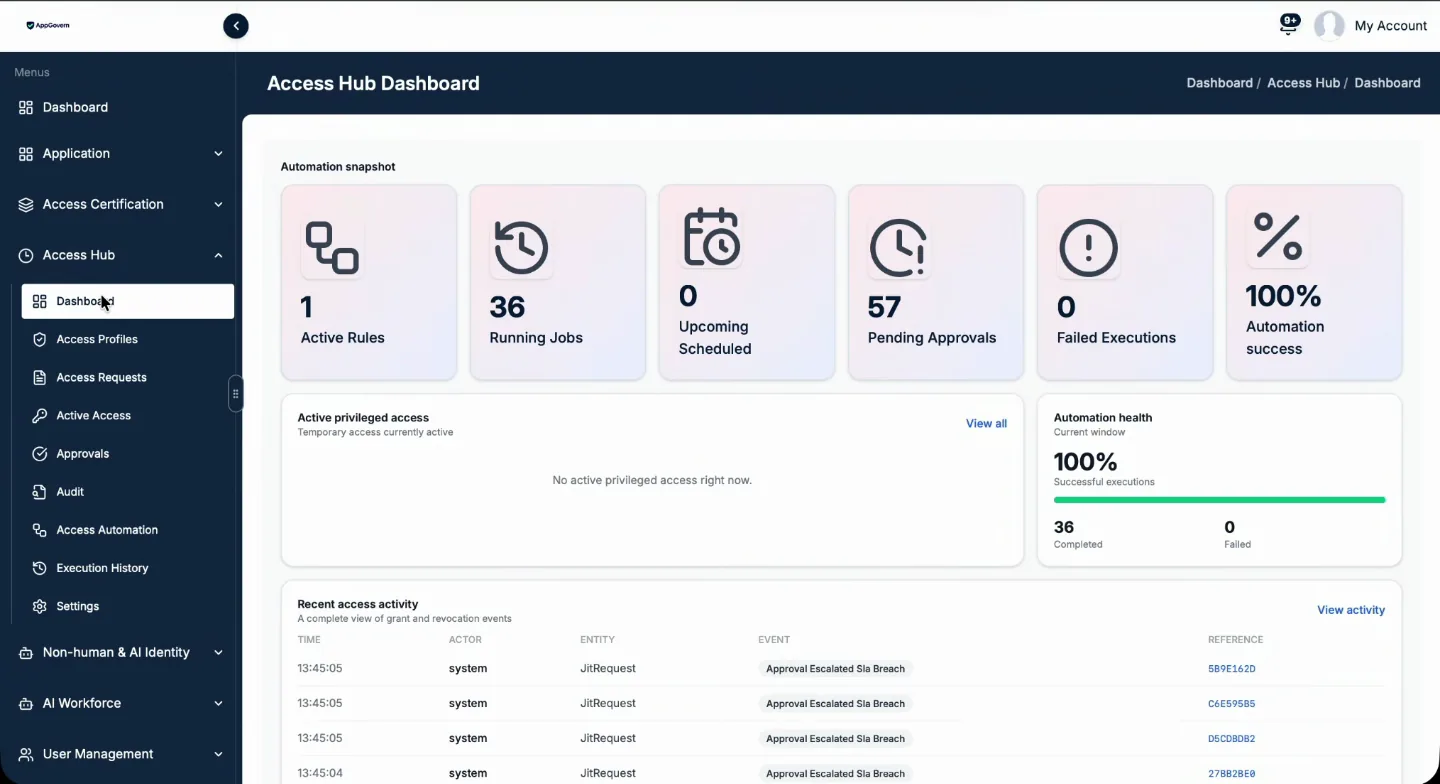
Access Hub: active rules, pending approvals, and automation health.
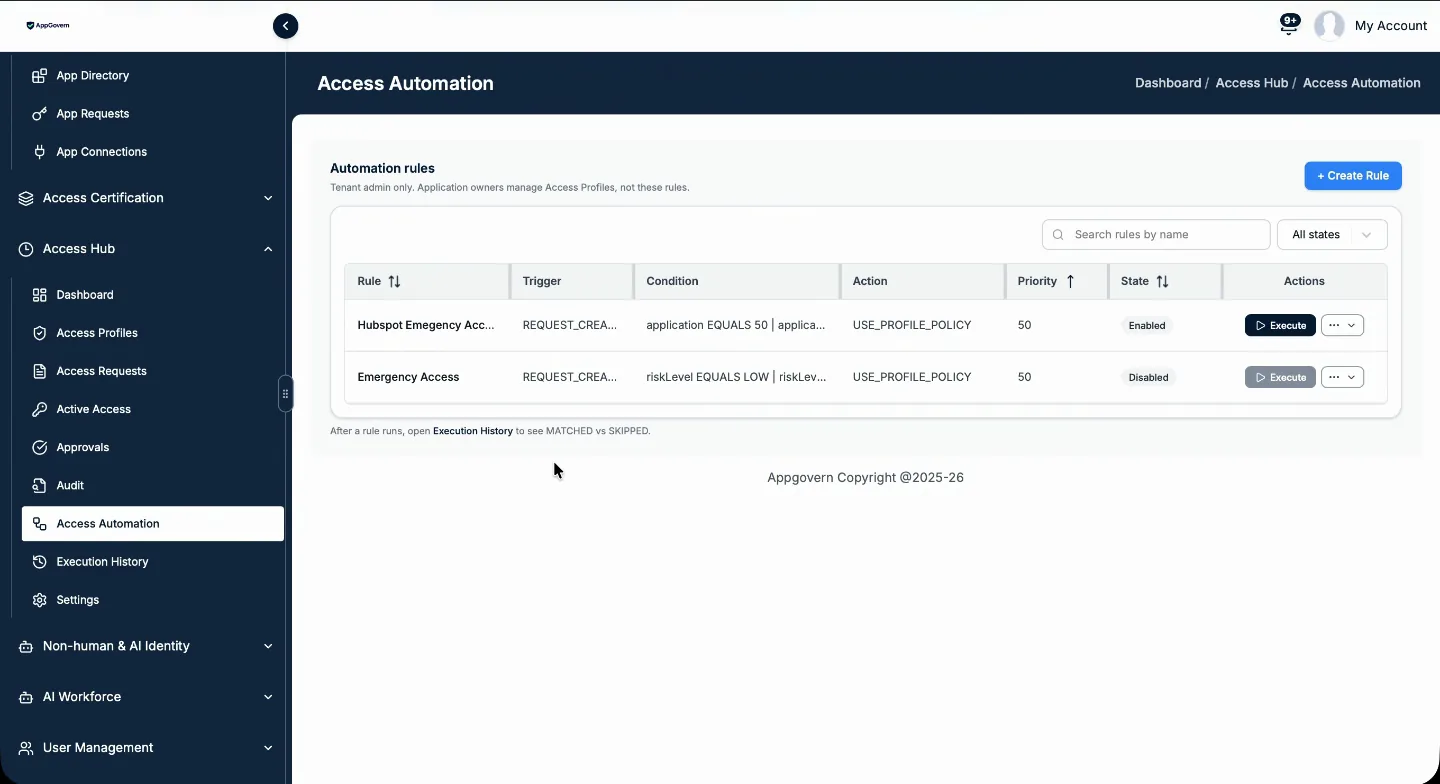
Access automation rules with trigger, condition, and action.
Chapters

What you will see.

Applications and shadow AIThe inventory builds itself from the identity provider and shadow signals.
OwnershipProbable owners proposed, accepted in writing.
AI agents and MCP serversThe relationship graph from workflow to tools.
Service accounts and local accountsDetected against HR, found inside the apps.
Just-in-Time accessRequested, approved by the owner, revoked on its own.
Certification and evidenceThree layers, then the export for the auditor.

Seen enough? Try it on your own data.

Free 14-day proof of concept. Read-only, success criteria agreed before we start, readout on day 14.